In the field
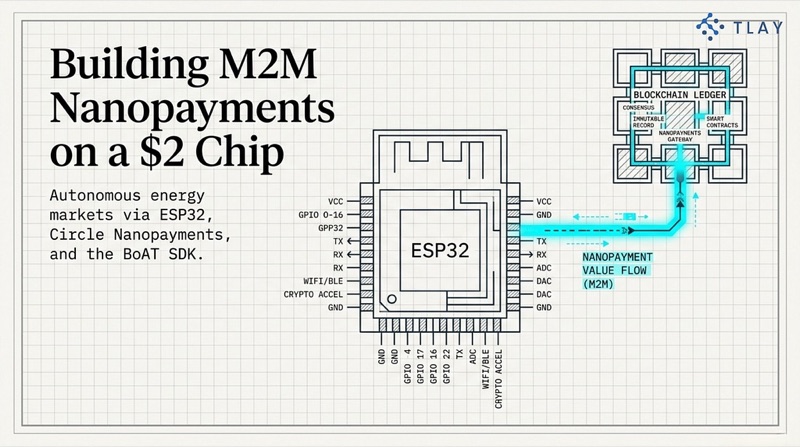
A tiny runtime that lets a machine prove what it measured and pay for what it uses — while the private key never leaves the chip.
Today a server signs for every device. To pay or be paid on its own, a machine needs a key of its own.
One account holds every key. Leak it and every device is impersonated; lose the network and nothing can pay.
It signs within limits its owner set, keeps working offline, and leaves evidence anyone can check.
A key made on the chip on first boot, never exported — and the address and DID that come from it.
Every reading hashed and signed at the source.
One signed stablecoin authorization per slice, within its owner's limits.
The buyer signs for each slice before the next one arrives — so neither side ever trusts the other with more than a fraction of a cent.
The seller broadcasts its price over Bluetooth.
The buyer checks rate, cap and window against its policy.
It signs one slice's payment, on the chip.
The seller delivers the slice. Repeat; settle in batches.
On your laptop, no hardware needed. Two boards come next.
$ git clone https://github.com/TLAY-IO/boat-mer.git && cd boat-mer
$ cmake -B build && cmake --build build
$ ./build/quickstart
…
recovered    0x76ebfd227d9fa763035fc31372f5923b52e014b3
result       OK — signature recovers to this device
cross-chain  correctly rejected